Bitrise was started in 2014 to make building and releasing mobile apps easier and faster. More than 8,500 mobile teams trust Bitrise, and we want to keep that trust. That is why we are sharing a full and transparent review of the security incident.
On November 13, we detected suspicious activities with regards to a bot account that had access to our internal system running CI builds for build steps. Four hours later, we turned off the whole platform.
We have addressed the security risks, and Bitrise is safe to use. Most services are back to normal.
From Friday on, most of the company worked on nothing but the incident. Engineers from every product and infrastructure team worked with security, support and customer teams in shifts across Europe and the US, with a short call every few hours so everyone shared a single unified operational context. Support updated the status page almost every hour, around the clock.
We’re also publishing a technical advisory with what we observed during the attack: their IP addresses, user agents and sign-up patterns, how they tried to use decoy. The attacker’s indicators are also included as CSV and STIX files for threat response tools for import. Other teams can use them to check their own systems for the same attacker or patterns.
What you should do now
Before we go into the details, here’s what we recommend now. While we have no indication customer secrets were accessed in any way, out of an abundance of caution we suggest rotating the secrets you store in Bitrise. The attackers took some of Bitrise’s own secrets, not related to customers, from our CI workflows. Based on the log analysis of the attack, we have no indication of customer secret store access, nor attempts to access customer secret store.
Unfortunately, with the advance of AI accelerated attacks, we expect more such incidents to happen across the board. What we can do is to be prepared for fast response and rapid secret rotation. We are here to help our customers with that.
Suggested steps:
- Rotate secrets, tokens and certificates stored in Bitrise, and the Git credentials connected to it.
- You can find your secrets: Workflow Editor > Secrets and under Workspace settings > Shared resources.
- To help identify your secret values to rotate, we released the Protected Secret Masked Review, which doesn't rotate anything for you. Click the eye icon in the field to reveal the last 4 characters. As you see below.
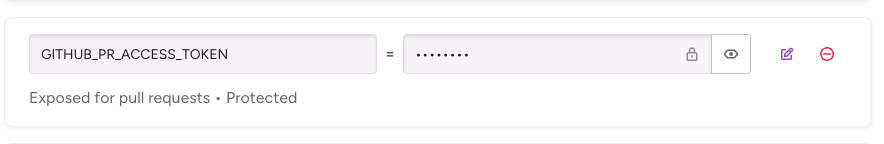
- Authorize the Bitrise GitHub App again if your projects use it. On November 13 we replaced the private key of the Bitrise GitHub App and revoked all user authorizations for it. If enabling GitHub Checks or linking additional repositories fails with a 422 error, authorize the Bitrise GitHub App again on your Bitrise account.
- Reconnect your GitHub OAuth connection in Bitrise. On November 13 we revoked every access token issued by the Bitrise GitHub OAuth app and rotated its client secret. This disconnected every Bitrise account that was connected to GitHub through OAuth. If your projects use the OAuth connection rather than the Bitrise GitHub App, reconnect your GitHub account in Bitrise to restore the connection.
- Re-add your SSH key if your project uses SSH and a build can’t clone your repository. This only affects projects that use an SSH key to access the repository. When the OAuth tokens were revoked, GitHub automatically removed any SSH deploy keys that Bitrise had added to your repositories with them. Keys you added to GitHub yourself were not affected. If the Bitrise key is missing, configure it from your repository’s Settings > Deploy keys in GitHub, re-add the project’s SSH key in Bitrise after reconnecting your GitHub account.
- Not related to the incident: As a best practice, review your public install pages. They allow without signing in, by design. Turn off any you no longer need.
What was accessed and what wasn't
We know the first thing you want to know is whether your workspace was affected, so here’s what we found.
Most of what the attacker accessed was Bitrise's own: internal credentials, some of our repositories, and operational records like infrastructure configuration and build machine logs. Those records mention customers by name or ID in places, but contain no customer confidential data.
Files in 15 customer workspaces were accessed without authorization.The attacker downloaded:
- 1 code-signing certificate file, but could not access the password for it that is stored in the secret manager to open it,
- 1 provisioning profile, and
- 13 diagnostic build logs from May 2026 containing short snippets of source or test code, a few lines at a time. One log contained a credential, and another one an email address.
All 15 customers were contacted immediately.
For every other workspace, our file-level in depth analysis found no evidence of the customer's secrets, code-signing files, build artifacts or source code in what the attacker accessed.
We are waiting for audit logs from GitHub to correlate with ours before we can move to close the investigation and enter the final report phase.
Timeline and how the attacker got in
Our investigation has linked the attacker to scanning and probing between October 25 and 27, 2026. During that period, they scanned more than 20 Bitrise hostnames and registered test accounts using disposable email addresses. This is a typical pattern we see all the time. Some of their tools described themselves as authorized penetration tests or security research, but those labels were supplied by the attacker without authorization. Practically, the attacker during their discovery blended in to business as usual customer initiated legitimate scanning activity.
During their discovery the attackers accessed one of our customers’ public applications that they use for their own penetration testing workflows, falsely establishing connection between the adversarial scan and legitimate pentest activity. We found this a sophisticated way of trying to decoy actual adversarial scanning and discovery activity.
On November 12 at 14:00 UTC, the attacker created a new account to run builds containing their own scripts against a public placeholder repository, running the same decoy patterns described above. Those scripts probed the build environment for credentials, and used said credentials to test those for cross-account listing vulnerabilities. All those requests were refused. This still seemed like a normal pentest pattern. The activity on this day happened between 2026-11-12 12:52 and 19:19. Then pause. Up until now, no out of the norm suspicious activity happened.
The day of the attack – The attack moved fast
The next day, on November 13 at 16:32 UTC, we detected suspicious activity.
The entry point was an internal Bitrise testing bot user account ([email protected]) used within a workspace designated for building and testing build steps. The attacker gained access by supplying the valid username and password combination; how those credentials were obtained remains under investigation. Originally configured to validate authentication with the Apple Developer Portal via AppleID, the bot account lacked two-factor authentication (2FA), a critical oversight that allowed initial entry. Once inside, the threat actor extracted additional credentials from the account to expand their access, executing an enumeration and privilege escalation scheme they had prepared over previous weeks. We are going to share more details in the final report, but wanted to share here early in the preliminary that we identified how the attackers got in.
During the early hours of the incident, we disabled all bot accounts, reviewed their credentials and 2FA settings so that this does not happen again. The initial attack vector was closed at that time.
We declared a SEV-1, our highest incident level at 17:42. As we did the live investigation initially, the attack seemed to be contained, but new results came in and facts were changing by the minute. We were correlating these realtime, but felt we were falling behind on the response curve to contain. When we saw evidence of unauthorized access in our GitHub repository, I made the call in the incident meeting to initiate “shutdown protocol”, turning off everything to contain the attack. At 19:26 UTC, we started shutting down our backend systems, database, secret access, all data centers, and GitHub access to stop any further possible exfiltration. We switched off the platform at 20:34 UTC.
Making that call in the middle of a fast-moving situation was one of the hardest choices I’ve had to make, yet it remained the single most effective action to immediately sever the attacker’s foothold.
Over the next two days, our engineers worked around the clock in shifts, and the whole company joined them. We rebuilt our build infrastructure from trusted sources both Linux and Macs. Thousands of servers on two continents in three data centers.
We think Bitrise was a target because it holds credentials for many companies in one place, which makes it worth an attacker’s time. In about half of this year’s supply chain incidents where the attacker’s goal was known, they were after credentials and secrets. Our evidence doesn’t show whether the attack on Bitrise is connected to any other incident, so we won’t speculate.
I shared a detailed technical advisory with everything we found in our logs. We wrote it for security teams, because the same attacker may target other companies. It lists the attacker's IP addresses, user agents and sign-up patterns, so your team can search your own logs for them. It also shows each step of the attack, from a normal sign-up to stolen credentials, and suggests an alert that would catch each one. The indicators come as CSV and STIX files that your security/threat-response tools can import directly, and you are free to share the advisory with anyone.
How we contained it
In addition to switching off the whole platform, we immediately started rotating all secrets, tokens, certificates from systems to contain this, in case anything was leaked that we had no proof of at the time, due to the speed of the attack and exfiltration attempts. We did not leave it to evidence based key rotation, we moved to nuke everything immediately.
From then on, we treated every part of the Bitrise platform as untrusted until we had rebuilt or reviewed it:
- We revoked access everywhere, including credentials we had no reason to suspect: all potentially affected access tokens and sessions, every token and key for the Bitrise and Bitrise - Build Hub GitHub apps, and all 919 of our cloud service account keys.
- We rotated all Bitrise-managed production secrets and credentials, not only the ones we knew had been touched.
- We brought each service back only after its credentials were rotated and it passed our security review.
Recovery phase
We artificially slowed down the requests coming from the attacker's IP addresses (tarpit) and kept watching activity during service recovery. The attacker kept probing for about a day after the shutdown. We've seen no successful unauthorized access since containment, and monitoring continues.
By implementing a tarpit to deliberately slow incoming requests, we brought the log stream down to a level suitable for “human-scale inference.” This allowed us to analyze the attacker's intentions and evaluate the impact in real time alongside the threat response team during the incident call. This process would be impossible against the high volume and rapid speed of requests produced by a swarm of AI agents. Although we successfully isolated the generated noise, tracking the rapid shift in targets, probes, and unauthorized access proved difficult. When system expertise is fragmented across multiple team members rather than held by one individual with complete end-to-end visibility, recognizing the broader pattern as it unfolds becomes a significant challenge.
In the current era, we need machine-scale inference speed for detection and response to have any chance of stopping these attacks. The normal speed of opening an incident, reviewing, discussing, and making decisions by humans are too slow to mitigate the threats with the current state of AI accelerated tools. We learned the lesson.
During recovery, we also built multiple monitoring agents collecting data from different sources and cross-referencing information to detect new attacker activity, using the recent learnings. Having prior experience of how to configure, run and scale agents in the team came very useful.
Which Bitrise services are back
Most services are running normally. status.bitrise.io has the current state of each one.
Services came back one at a time, in the order you needed them. Builds returned for workspaces with a paid subscription a little over two days after the shutdown, and the remaining services followed in stages.
The recovery had rough edges you felt directly: integrations to reconnect, deploy keys that GitHub removed, and queues while capacity came back. New account sign-ups are paused during recovery. If you need an account added, write to [email protected] and we'll arrange it.
It is safe to build and release again. All systems were rebuilt from scratch from trusted sources, all Bitrise-managed production credentials were rotated, and every service passed a security review before it returned. If your security team wants to talk to ours before you resume, we'll set up a call.
What comes next
The forensic investigation and system hardening continues internally. We engaged with multiple independent digital forensics and incident response firms to verify our findings and actions, which we’ll share with our customers.
We're waiting for audit logs from GitHub, to correlate against our own findings, which is our last blocker before the final report. It will be published as soon as possible.
How to reach us
- Questions about your account or the incident: your usual Bitrise contact, or [email protected]. If we've already contacted you about your workspace, reply to that email.
- Security teams: [email protected]. Our security team and leadership are available for security-to-security calls. Please don't send secrets, tokens or personal data that isn't needed to identify an event.
- Service status: status.bitrise.io.
We know these days were hard for your teams too, with secrets to rotate and integrations to reconnect on short notice. We’re doing everything we can to protect you and the system.
Thank you for your patience, and for the messages of support many of you sent us. We are sorry for the disruption this caused, and we will keep sharing what we learn.
Get started for free
Get a 30-day free trial and join the 400,000+ mobile developers who already love Bitrise.
Start free trial